Welcome to our EU site – choose your Jurisdiction

EU AI Act Compliance Services

AI without compliance isn’t vision. It’s vulnerability.
Bridge the gap between rapid deployment and total regulatory control.

Artificial Intelligence (AI) is unquestionably a defining force in today’s society. Organisations are embracing its benefits, but often overlook the risks that can gradually surface and disrupt their business.

Deploying artificial intelligence without legal guardrails transforms your greatest technological asset into your largest enterprise risk.

The EU AI Act is the world’s first comprehensive law governing artificial intelligence. Through a single legal framework, it regulates AI systems across the EU, promoting human-centric and trustworthy AI. Does your organisation develop, deploy, or use AI systems in the EU? Compliance isn’t optional, it’s a responsibility!

Organisations within the scope of EU’s AI Act

The AI Act assigns responsibilities at every stage, providers build compliant systems, importers and distributors verify compliance, and deployers ensure correct use. These obligations span both public and private sectors, including:

Financial Institutions

Governmental Digital-Services Departments

Hospitals & Healthcare centres

Universities, Schools and Training Institutions

Police and Border-Control Authorities

Insurance Companies

Tele
communication Providers

Critical Infrastructure

AI Developers and Tech Providers

Retail, Tourism and Hospitality Businesses

Media, Marketing and Content Creation Companies

Migration and Asylum Authorities

Courts and Judicial Authorities

Recruitment Agencies

Key Element of the Regulation

The AI Act is built on six key elements that together shape how AI is regulated across the EU.

  1. Harmonised rules for placing on the market, putting into service, and using AI systems.
  2. Prohibitions on specific AI practices.
  3. Special requirements & obligations for high-risk AI systems.
  4. Harmonised transparency rules for certain AI systems.
  5. Market monitoring, surveillance, governance & enforcement rules.
  6. Innovation support measures, with a focus on SMEs, including startups.

Complyport EU Services: Start Your Compliance Journey Today

We strip away regulatory complexity to deliver clear, actionable, and low-friction compliance frameworks. Our team supports organisations navigate the AI Act with clarity, confidence, and minimal disruption to operations.

AI Act Diagnostic & Gap Assessment

  • Applicability and Organisational Roles: Determine which AI Act obligations apply based on the organisation’s AI activities and roles, whether acting as a Provider, Deployer, Importer, or Distributor.
  • Risk Classification and Prohibited Practices: Classify AI use cases, deployments by risk level and identify prohibited practices.
  • High-Risk AI Systems: Review applicable controls covering risk management, data governance, documentation, accuracy and human oversight.
  • Provider and Deployer Obligations: Identify the responsibilities applying to the organisation as an AI provider or deployer.
  • Transparency Obligations: Check whether individuals are properly informed when interacting with AI-generated or manipulated content.
  • Control and Evidence Validation: Verify through documentation and stakeholder discussions whether AI controls operate effectively in practice.
  • Fundamental Rights Readiness: Determine whether an Article 27 assessment (Fundamental Rights Impact Assessment) is required and review how potential harms to affected groups are addressed.
  • Remediation Roadmap: Provide prioritised findings and potential impact on regulatory readiness. Recommended actions and target timeframes will be identified to address compliance gaps and weaknesses.


Scoping and Documentation Review

Gain 100% visibility over every AI system deployed across your enterprise.

  • Review each AI system /AI use cases, system inventories, purpose policies, ownership, procedures, and governance documentation,
  • Establish project boundaries and define implementation requirements tailored to your framework.

AI Governance Framework Implementation

  • Design and implement compliant AI policies aligned with the AI Act.
  • Establish clear roles, responsibilities, and explicit decision-making authority across all AI initiatives.
  • Establish mechanisms for identification, assessment, mitigation and escalation procedures for emerging regulatory risks.
  • Utilise ISO 42001 as the structural framework to achieve and maintain the operational requirements demanded by the EU AI Act.
  • Prepare your organisation for third-party ISO 42001 certification to build trust with clients and stakeholders.

Enterprise AI Act Training

  • Build an AI-literate workforce equipped to navigate regulatory requirements and mitigate risk.
  • We deliver concise, tailored presentations and interactive seminars customized to specific operational roles and executive tiers.
  • Prohibited Practices & Risk Boundaries: Clearly define banned AI practices and help teams identify non-compliant usage scenarios.
  • Safe AI Adoption: Equip employees with practical guidelines for safe, trustworthy, and responsible day-to-day AI use.

The AI Act assigns responsibilities at every stage, providers build compliant systems, importers and distributors verify compliance, and deployers ensure correct use. These obligations span both public and private sectors, including:

Security shield with a red checkmark indicating verified protection on a light gray circular background

Frequently Asked Questionss

The AI Act is the world's first comprehensive law governing artificial intelligence. It aims to promote the development and adoption of trustworthy AI across the EU market, while safeguarding health, safety and fundamental rights, including democracy and the rule of law.

The AI Act applies to providers, deployers, importers and distributors of AI systems placed on the EU market or whose output is used within the EU, regardless of where the company is headquartered. This includes organisations in critical infrastructure, employment, credit scoring, law enforcement and several other regulated sectors.

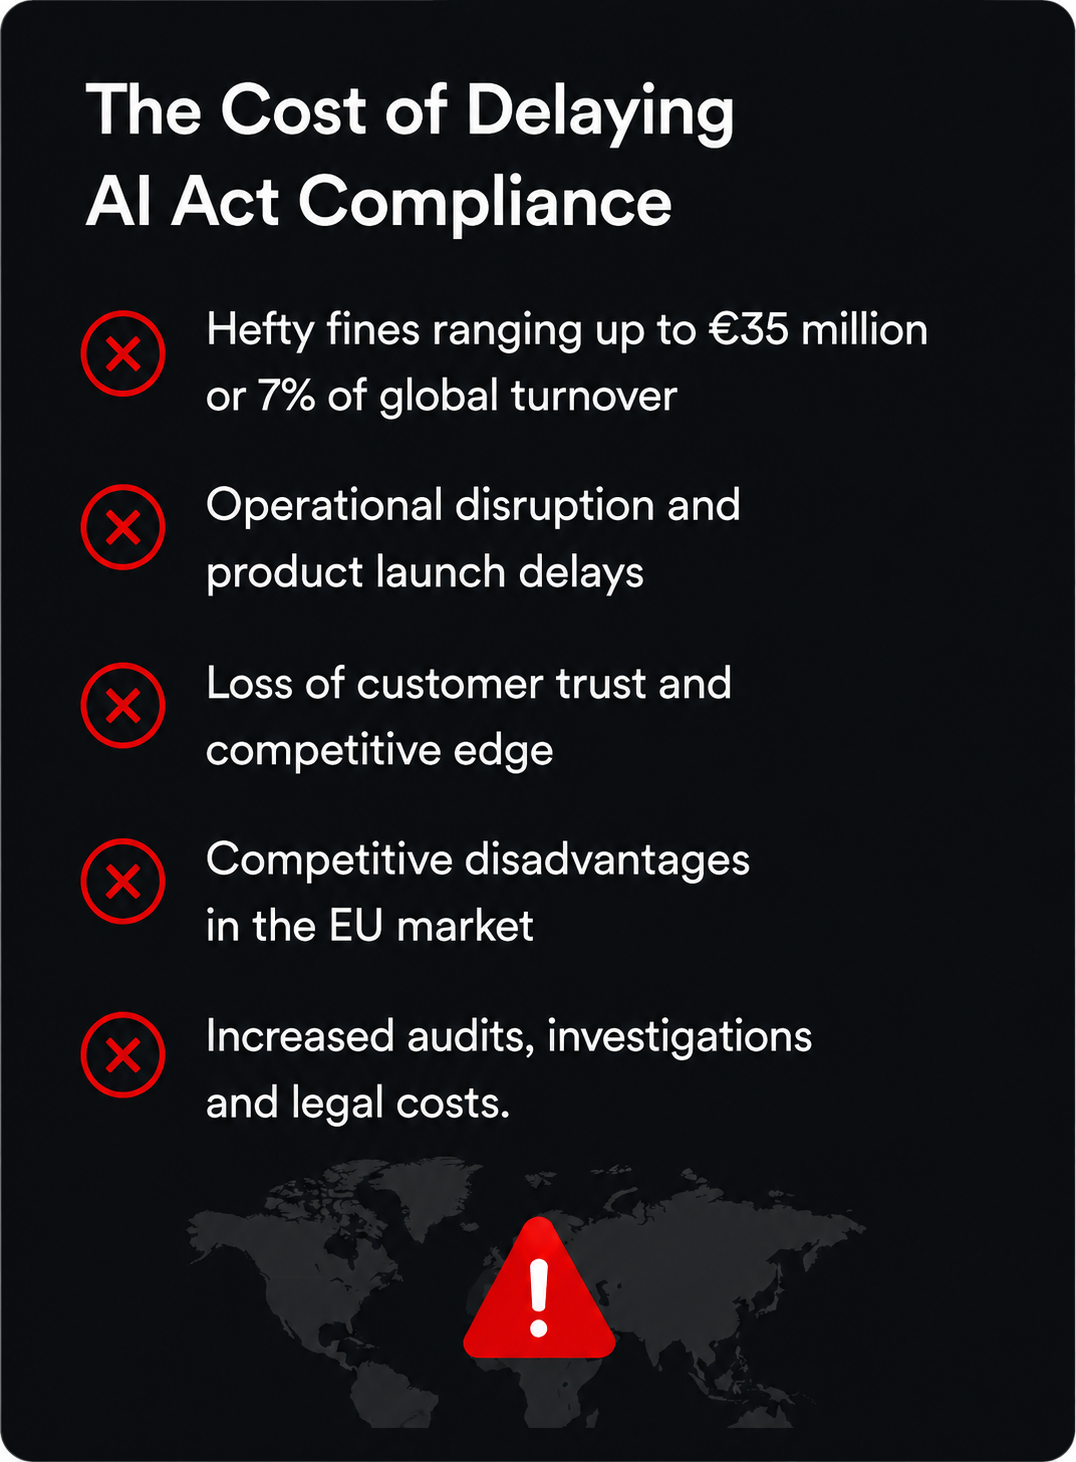
Non-compliance can result in significant administrative fines, ranging from €7.5 million or 1% of global annual turnover for supplying incorrect information, up to €35 million or 7% of global annual turnover for breaches of prohibited practices. Competent authorities can also require corrective action or restrict a system's use.

Risk management under the AI Act must remain active and be updated throughout the operational life of a high-risk AI system. Reviews should also take place whenever new risks emerge from post-market monitoring data or when the system is significantly modified.

ISO/IEC 42001 is a voluntary international standard, while the AI Act is a binding legal framework, so certification alone does not guarantee compliance. In practice, however, the two work well together: the AI Act sets out what organisations must achieve, while ISO/IEC 42001 provides the governance structure to help them get there, covering areas such as risk management, documentation, and human oversight. It does not, however, replace EU-specific requirements like the Declaration of Conformity or CE marking for high-risk systems.

Our Expert

Our subject matter experts bring together a wealth of backgrounds, skills and expertise from the financial industry, legal sector and regulatory bodies.

Pantelis Angelides

Managing Director – Cybersecurity and Operational Resilience

Why choose Complyport?

Extensive Regulatory Expertise

With over 25 years of experience in the financial services industry, Complyport offers unparalleled expertise in regulatory compliance, ensuring your firm stays ahead of evolving regulations.
Comprehensive Service Offering

From AML audits to risk management and regulatory reporting, Complyport provides a full spectrum of compliance services, allowing you to streamline your compliance processes and focus on your core business activities.

Tailored Compliance Solutions

We provide bespoke compliance solutions that are specifically designed to meet the unique needs of your business, ensuring that all regulatory requirements are met efficiently and effectively.

Client-Centric Approach

We provide bespoke compliance solutions that are specifically designed to meet the unique needs of your business, ensuring that all regulatory requirements are met efficiently and effectively.

Senior-Level Guidance

Our team of seasoned professionals, including former regulators and industry experts, leads all engagements, offering deep insights and practical advice to help you manage compliance risks effectively.

Innovative Fintech, Regtech, and AI Solutions

Leveraging cutting-edge fintech, regtech, and AI tools, Complyport enhances your compliance processes with advanced technology, ensuring accuracy, efficiency, and real-time regulatory updates. Our innovative solutions empower your firm to stay compliant while maximising operational efficiency.

Key Figures

Over 25 Years

Providing Compliance
Excellence

Over 1,500

Successful FCA, EU and UAE
Authorisations

Over 1,000

Active Firms Receiving
Regulatory Support

8 Lots

FCA/PRA Skilled Person
& Consultancy Panel

Get In Touch